The person who leaked the PHP vulnerability to Hacker News has apologized, saying they 'didn't know it was confidential.'
Tell HN: I unknowingly broke the PHP RCE embargo. I am sorry. | Hacker News
https://news.ycombinator.com/item?id=50193416
In a Hacker News discussion post titled 'Tell HN,' a user named petecooper posted on October 20, 2026, that 'According to a reliable source, an announcement regarding two PHP RCE vulnerabilities with a CVSS (security severity) score of 10.0 is scheduled for October 22, 2026 at 18:00 CEST (October 23, 1:00 JST).' Petecooper quoted his source as saying, 'While there is no concrete evidence, if you are using PHP in a production environment, you should prioritize preparing to update.'
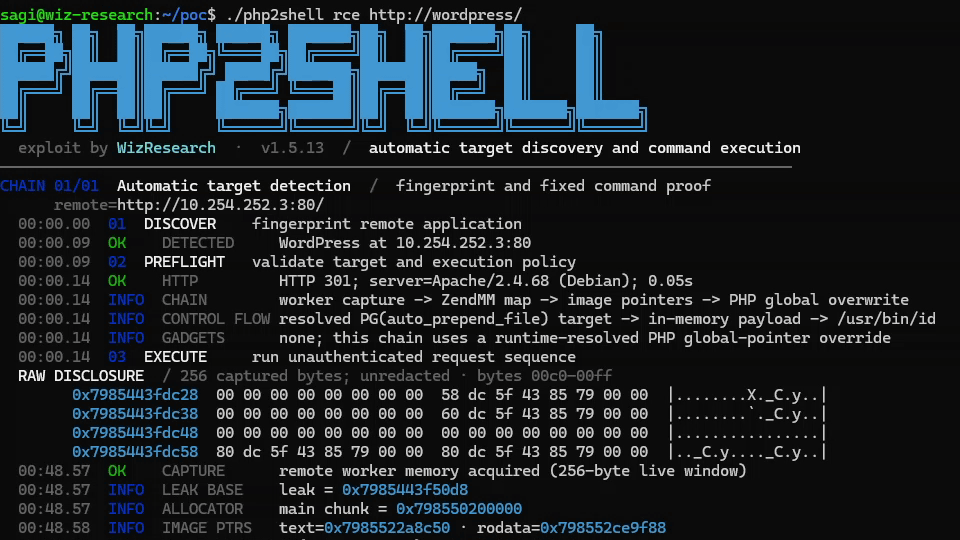
The two critical PHP vulnerabilities known as 'PHP2Shell' were reportedly discovered independently in August 2026 by security firms Calif and Wiz. The PHP security team had planned to release an update, but the vulnerability identification numbers and release schedule spread before the patch was released. Subsequently, videos demonstrating attack methods were also leaked, increasing the risk of unpatched PHP being targeted by attackers. Then, Calif mistakenly released a proof-of-concept video demonstrating the vulnerability, which was later removed but spread on social media. Furthermore, other researchers reported reproducing the vulnerability based on the released information, revealing details of the vulnerability before the patch was released.
Petecooper's post received critical replies such as, 'Vulnerability information is supposed to be kept secret,' and ' Announcing it in this way is like encouraging everyone to use their agents to find and exploit the vulnerability.' On the other hand, some commented that 'it has already been discovered and spread on X,' and that it should be widely known so that site operators can take action before a patch is released.
As a result, the PHP security team announced that they would release an emergency security update ahead of schedule on October 21, 2026. Various Japanese websites also temporarily went into maintenance mode to apply the emergency patch, and ultimately, emergency updates '8.5.12,' '8.4.27,' '8.3.36,' and '8.2.35' addressing PHP2Shell were released at 11:00 PM Japan time on October 21, 2026.
PHP releases emergency updates '8.5.12', '8.4.27', '8.3.36', and '8.2.35' - GIGAZINE
Subsequently, petecooper posted again on Hacker News' 'Tell HN,' apologizing and stating, 'I understand that my post about the PHP vulnerability has significantly impacted the information disclosure schedule and increased the workload. I am truly sorry and take full responsibility for my actions.' At the time of his post, petecooper was unaware that an embargo (information disclosure prohibition period) had been set for this vulnerability, and had been told by the informant and their informant that there was no embargo. As petecooper himself compiles from source code according to the PHP release cycle, he intended to make people in a similar position aware of the importance and urgency of the update.
Many voices on Hacker News defended petecooper, with comments such as, 'He can't be held responsible for breaking an embargo he wasn't informed about,' and 'You only reacted to information that was close to you, so you should object to the idea that you're taking full responsibility.' Petecooper stated, 'Some media outlets are reporting that what I posted in good faith led to the lifting of the information ban and the changes to a pre- agreed schedule. I haven't been able to sleep well since then. Apologizing and acknowledging my responsibility is my new course of action. I hope I can sleep tonight.'
Furthermore, Petecooper is a freelance consultant and has no connection or partnership with any of the organizations involved in this incident.
Related Posts:

in Security, Posted by log1e_dh