Two PHP vulnerabilities with a severity rating of '9.2' have been discovered, raising concerns about server hijacking. An emergency patch will be released on October 21st.
Two serious vulnerabilities have been discovered in PHP, a programming language widely used for developing websites and web applications, and the development team has announced that they will release an urgent security update on October 21, 2026.
PHP: News Archive - 2026
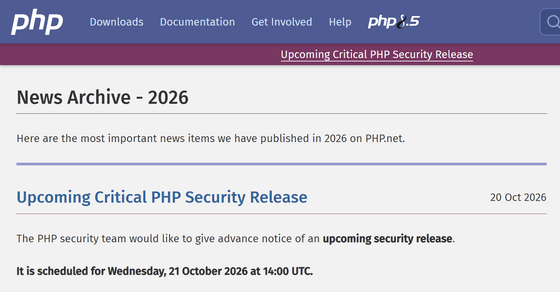
php.announce: [ANNOUNCE] Upcoming Critical PHP Security Release
https://news-web.php.net/php.announce/509
CERT-EU - Critical Vulnerabilities in PHP
https://cert.europa.eu/publications/security-advisories/2026-018/
PHP Remote Code Execution FAQ: CVE-2026-109618 & CVE-2026-109619
https://watchtowr.com/intelligence/php-cve-2026-109618-faq/
PHP warns admins of two critical flaws, emergency patches coming tomorrow
https://www.bleepingcomputer.com/news/security/php-warns-admins-of-two-critical-flaws-emergency-patches-coming-tomorrow/
PHP is a programming language used in content management systems such as WordPress, as well as in online shops and corporate web services. It is responsible for processing web page display and database interactions on the server side, so if a serious flaw is found in PHP itself, it could affect many websites.
The vulnerabilities at issue this time are 'CVE-2026-109618' and 'CVE-2026-109619'. According to the security company watchTowr, both vulnerabilities could lead to 'remote code execution,' where an attacker could remotely execute arbitrary code on a server. If the attack is successful, information on the server could be read or files could be tampered with.
The severity of the vulnerabilities has been rated at 9.2 on the Common Vulnerability Scoring System (CVSS 4.0), classifying them as 'critical,' the most serious category.
The PHP development team issued a warning on their official website and mailing list on October 20, 2026, announcing that they would release a patch at 11 PM JST on Wednesday, October 21. They also stated that they might release the patch even earlier if details of the vulnerability become public or if actual attacks are confirmed. The PHP development team has not officially announced the affected versions or the technical cause, and plans to reveal details at the same time as the patch is released.
CERT-EU, which provides cybersecurity information to institutions and organizations within the European Union, has also issued an urgent alert. CERT-EU states that all versions of PHP from 5 onwards may be affected and recommends identifying servers and applications that use PHP and preparing to update as soon as a fix is released. If a prompt update is difficult, they suggest temporarily disconnecting applications exposed to the internet from external networks.
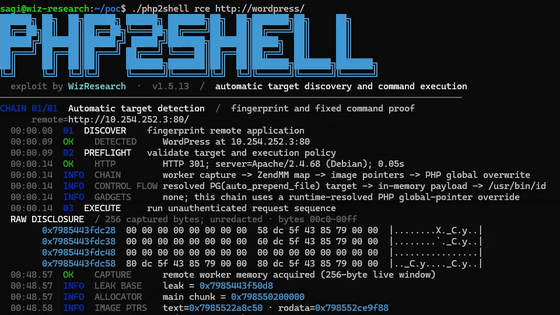
Meanwhile, security researcher Kirill Filsov posted a video on X, under the name 'php2shell,' that documented an actual attack. The video shows the attack being carried out against test environments using WordPress, Drupal, and Magento, and commands being executed on the servers. The attack is reproduced in multiple environments with different PHP execution methods, suggesting that it could affect a wide range of web applications.
php2shell
— Kirill Firsov (@k_firsov) October 20, 2026
Tomorrow is a helluva day. pic.twitter.com/M8ybQcrnlu
Security firm watchTowr has announced that it has successfully reproduced an attack using one of the two vulnerabilities, CVE-2026-109618. However, they are withholding technical details to prevent the exploitation method from spreading before the patch is released. They also stated that they have not seen any instances of this vulnerability being exploited in actual cyberattacks.
The PHP development team is urging administrators of websites using PHP to update as soon as the fix becomes available.
- Continued
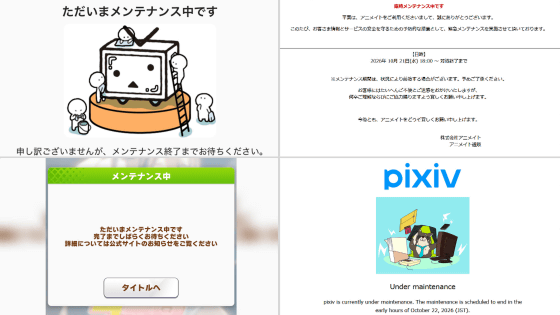
Various websites and apps, including Niconico and pixiv, are undergoing maintenance to support an emergency PHP patch - GIGAZINE
Related Posts:
in Security, Posted by log1d_ts